Why it matters
In 2026, researchers at ETH Zurich showed that a malicious server could swap public keys at several password managers and read what was shared. This is the defense.
Key transparency
To share with someone, your device needs their key, and it gets it from our server. Key transparency makes sure the server can't hand you a key of its own without being seen.
How it works
The server keeps an append-only log of each account's key. It can add to the log, never rewrite it.
When you find someone to share with, Vallkey checks the key it's given against the log, and shares nothing if the log doesn't back it up.
About once an hour, they check that the log has only ever held your key, and compare what they saw with each other.
The details
In 2026, researchers at ETH Zurich showed that a malicious server could swap public keys at several password managers and read what was shared. This is the defense.
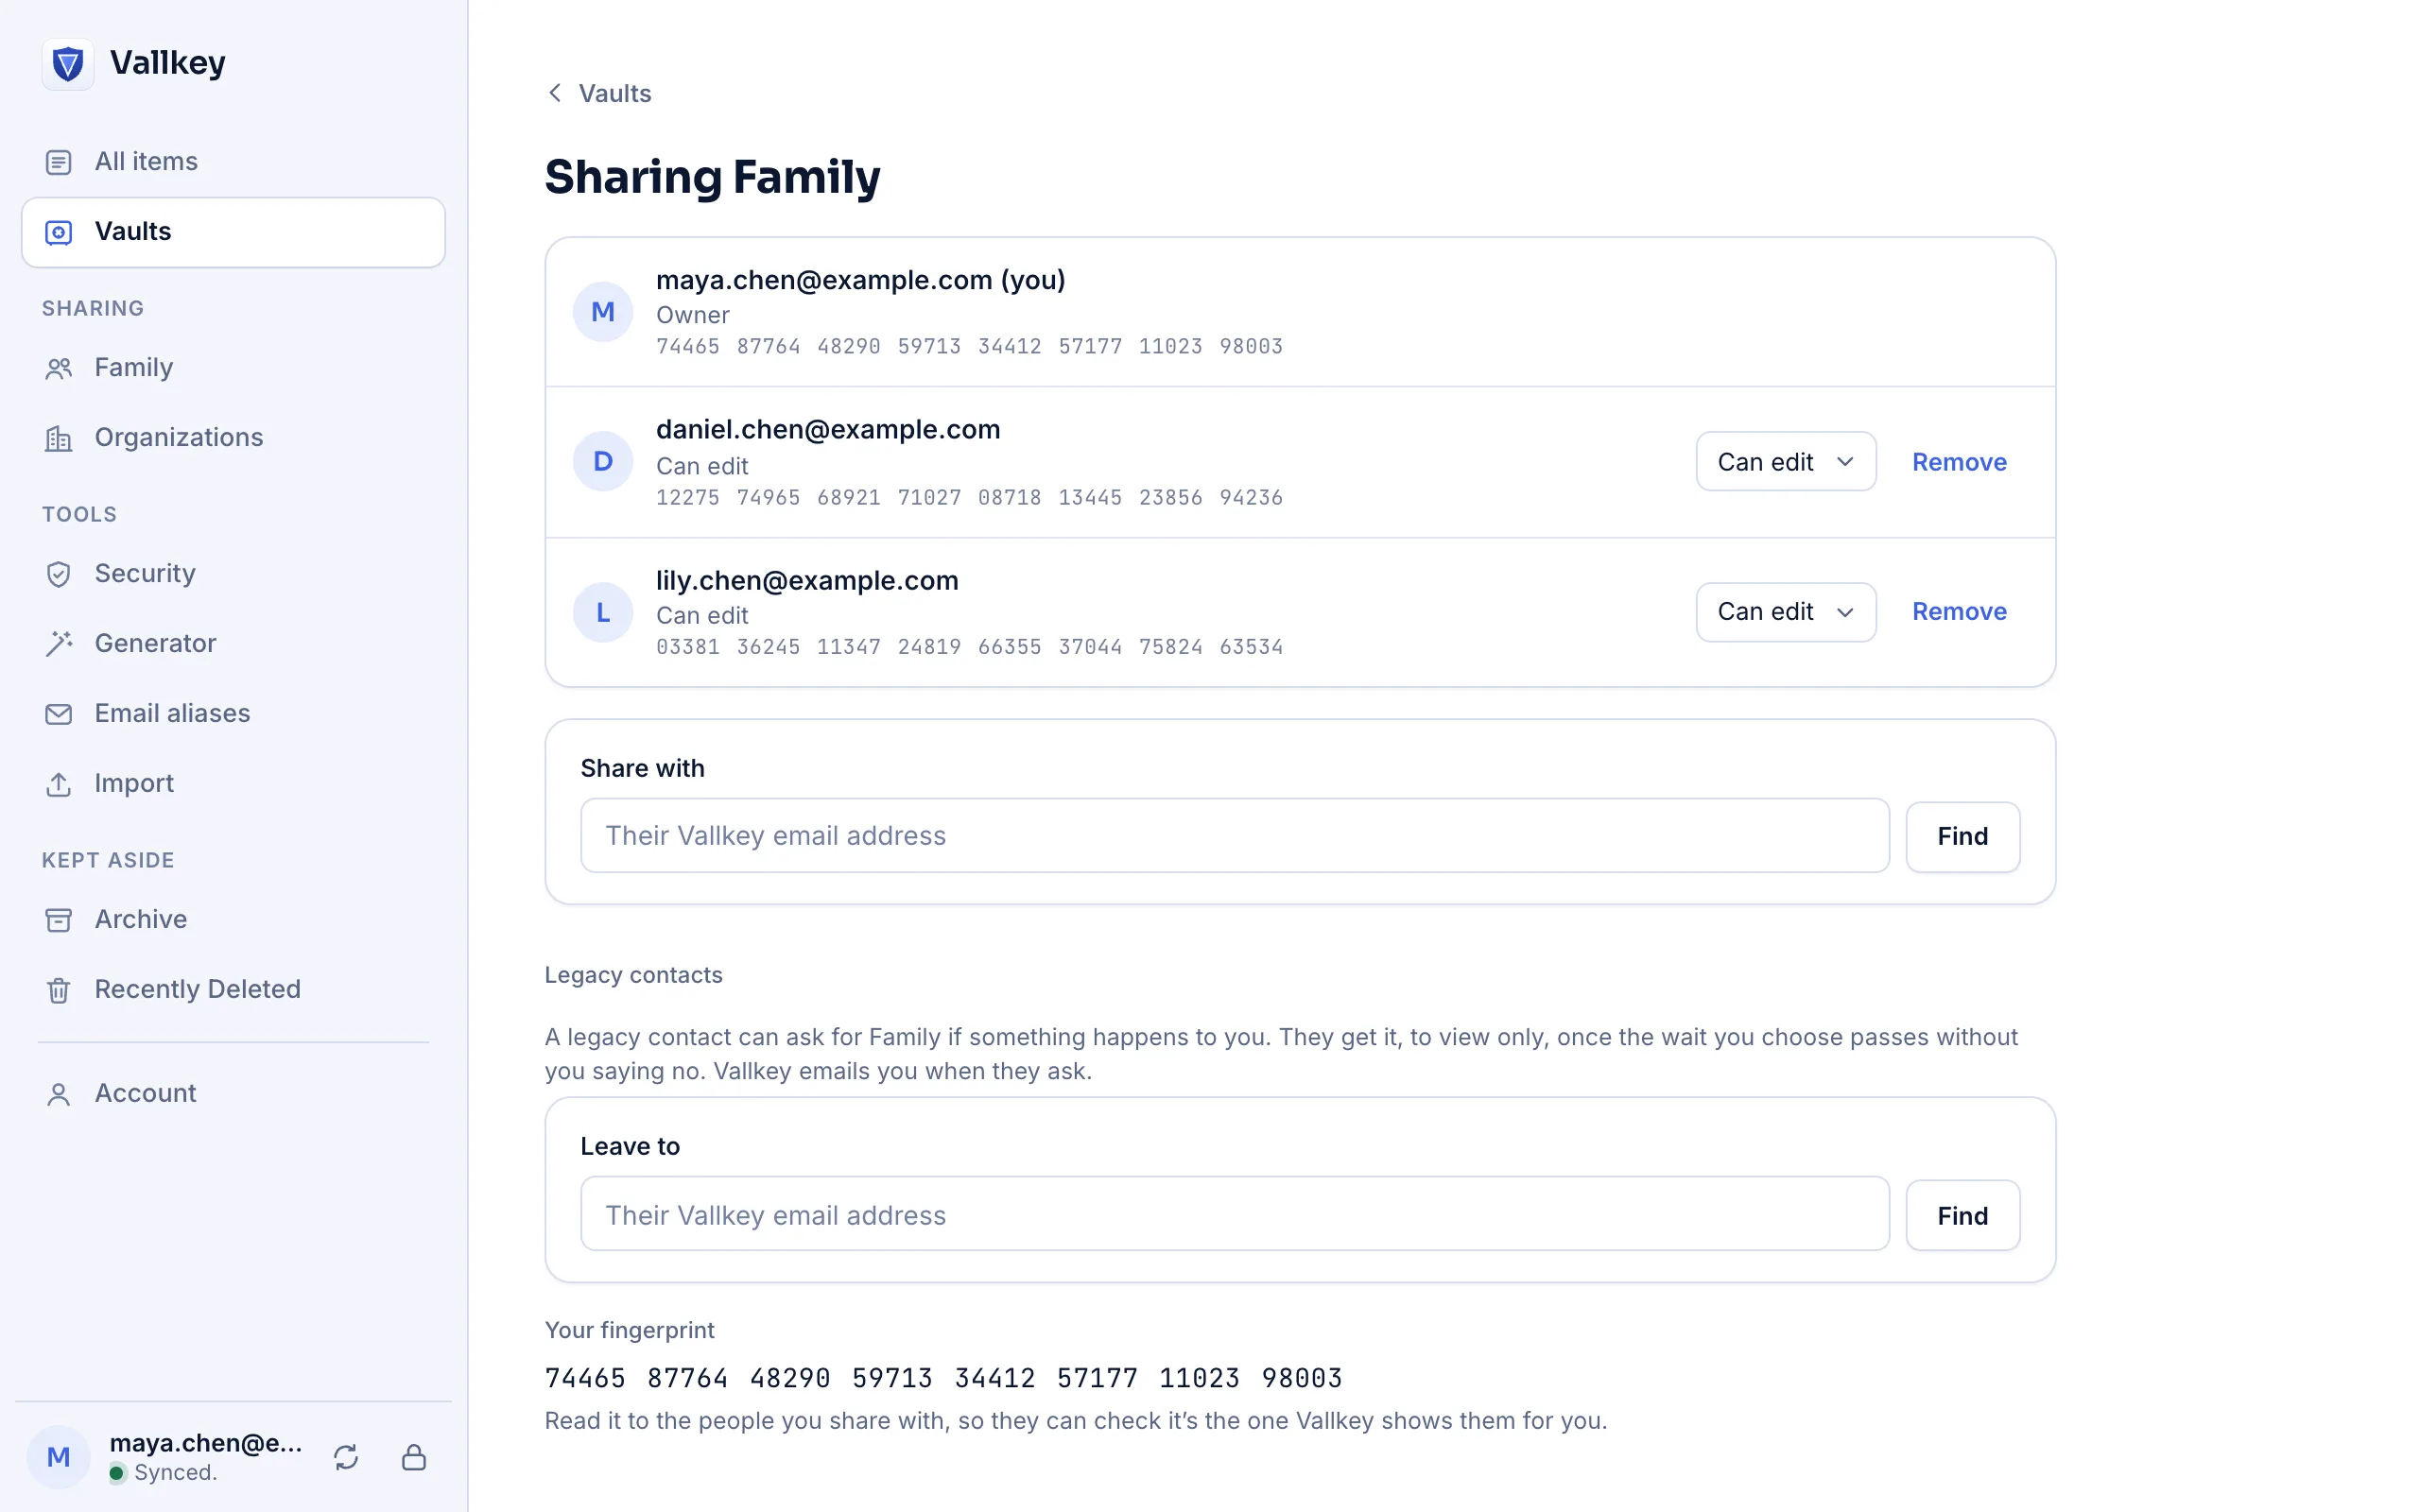
Compare a fingerprint in person or on a call, eight groups of five digits, and you're protected from the very first share.
The log publishes its signed heads, and proofs that it only grew, for independent auditors to check.
A brand-new device trusts the first log it sees. From then on, every change to anyone's keys is checked against it.
Availability
Nothing is shared with the key in question. Compare fingerprints with the people you share with, in person or on a call.
No. The checks run by themselves while you use Vallkey.
Vallkey opens soon. Join the waitlist to hear first.